|
|
 |
|
|
Competitive Overview (more analysis to be added from Rachels work)
|
|
|
|
|
Company
|
Product name
|
List Price
|
Web address
|
Venture Financing
|
|
Melior, Inc.
|
ISecure-ILS
|
$18,000 100MB
$45,000 1GB
$225,000 GigE
|
www.dos-protection.com
www.ddos.com
|
$0
($2,000,000 dev cost)
|
|
Arbor Networks
|
Peakflow DoS
|
$130,000 for base system
|
www.arbornetworks.com
|
$11,000,000
$22,000,000 (8/2002)
|
|
Asta Networks
OUT OF BUSINESS
|
Vantage System
|
$8,000 per router unit
|
www.astanetworks.com
|
$18,000,000
BURNED
|
|
Captus Networks
|
CaptIO/CaptIO-G
|
$45,000-$55,000
|
www.captusnetworks.com
|
$25,100,000
3RDCEO/RESTRUCTD
|
|
Mazu Networks
|
TrafficMaster Inspector & Enforcer
|
$100,000 for base system
|
www.mazunetworks.com
|
$20,000,000
|
|
Lancope
|
StealthWatch
|
$20,000
|
www.lancope.com
|
$5,550,000
|
|
Riverhead Networks aka Wanwall
|
WanWall
|
$70,000
|
www.wanwall.com
|
$16,000,000
|
|
WebScreen Technologies
|
WS100
|
$21,400
|
www.webscreen-technology.co m
|
$1,400,000
|
|
Toplayer
|
Attack Mitigator IPS
|
$15,000-38,000
|
www.toplayer.com
|
$28,000,000
|
|
|
|
|
|
|
|
|
|
NEW: Mirage Networks in Austin claims to be working on a similar product, previously announced to be due in mid-2003. They just changed their website, bringing it down to 3 pages. This is after we talked to their VC....Update Friday 5/9/03: Centerpoint invested apparently $200,000 (according to the Dallas Business Journal); we got Startech to spill the beans, and they said the total VC money is more like $7,000,000 (unconfirmed).
OTHER: Fortinent, from/with the original NetScreen developer Ken Xie, makes also claims to deliver wire-speed protection with FortiGate, an in-line firewall, anti-virus, IPSEC device (not IPSEC protocol initiation protection), which is based on an ASIC hardware platform. The anti-virus protection is policy- and library-based; it also offers traffic-shaping and signature-based intrusion detection. In their data sheet they claim dDoS protection as well, but under the section of IDS, while in the same section pointing out it is attack database driven - i.e. yet another signature-based IDS system, able to recognize only known forms of attacks. Seems like a nifty product, a competition against the NetScreen firewall.
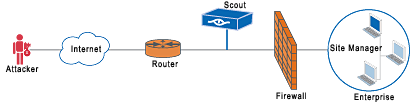
OTHER: ForeScout has a product called ActiveScout, which is a 3-phase pre-attack monitor. It sits outside the firewall, but on a separate connection (not in-line), and does a stateful TCP Intercept on suspicious traffic (it being stateful means it can be easily attacked and compromised). It will not identify an attacker, unless the attacker does a port scan first (recon activity) from the machine the attack is launched from.In other words, if the attacker does not scan first, or scans from one machine and attacks from another, ForeScout is worthless (ineffective); or: it intercepts by source IP. Logically, it is not effective against Denial-of-Service attacks.
|
|
|
 |
|
|
|
OTHER: 5/15/2003 Ciscos Security Agent is a product, which in essence comes from an acquisition (Okena Stormwatch); requires a Windows machine, and is a separate agent. Not any competition with iSecure, but may come up in product comparisons.
Key Benefits
- Aggregates and extends multiple endpoint security functions by providing host intrusion prevention, distributed firewall, malicious mobile code protection, operating system integrity assurance, and audit log consolidation all within a single agent.
- Provides preventive protection against entire classes of attacks including port scans, buffer overflows, Trojan Horses, malformed packets, and e-mail worms.
- Offers "Zero Update" prevention for known and unknown attacks
- Provides industry-leading protection for Unix and Windows servers and Windows desktops allowing customers to patch systems on their own schedule.
- Open and extensible architecture offers the capability to define and enforce security according to corporate policy.
- Scalable to thousands of agents per manager to support large enterprise deployments.
OLD: KarlNet, Inc.s Karlbridge is another product we are frequently asked about in comparison to iSecure. This product hardly compares at all to iSecure, just mentioned here to avoid someone else to look it all up again. The KarlBridge is essentially a brouter (bridge router), a technology used in the 1980s. Limited to a maximum of 100 Mbit/s, it does some packet filtering, as you find it in any Cisco router in an advanced form. That a Bob Cringely brings this product up for comparison against iSecure, makes me wonder if he understood the iSecure concept (I admit, that is a snide remark - Thomas).
|
|
|
|
Older Information:
|
|
|